The openness and freedom of the cryptocurrency world always come at a silent cost for someone.
Written by: Liu Honglin
In March 2024, an employee working at the Japanese wallet software company Ginco encountered a "recruiter" on LinkedIn. The recruiter sent him an onboarding test, asking him to handle a piece of Python code.
Job boards, code hosting platforms, and technical tests are all familiar to programmers looking for work. However, according to an investigation later released by the FBI and the Japanese National Police Agency, this interaction allowed the attacker to infiltrate the employee's device.
Two months later, the attacker used the stolen login session to impersonate this employee, gained access to the company's communication system, and likely manipulated a normal trading request from the client DMM Bitcoin.
Ultimately, 4,502.9 bitcoins were lost, worth about $308 million at the time of the incident. The individual who received this money did not appear as a masked robber. Instead, he entered your daily life pretending to be someone who might help you find a job.
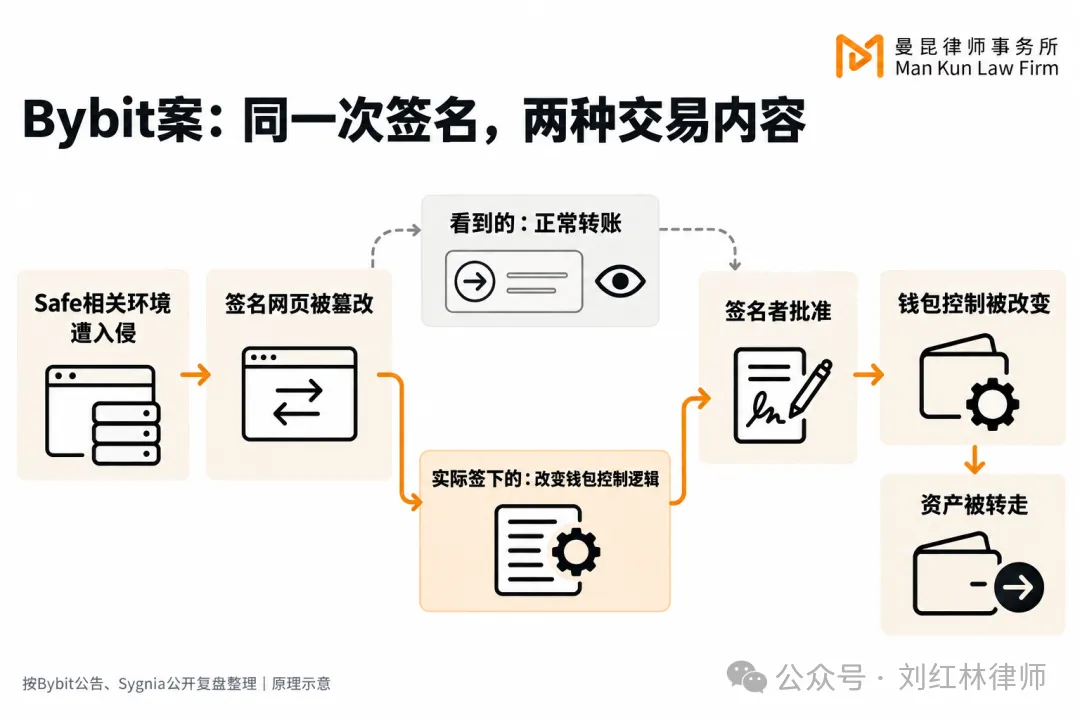
Path of the DMM case action
This also explains why discussing North Korean hackers today by simply saying "the technology is impressive" is no longer sufficient.
On October 31, 2026, the FBI attributed the theft of over $6 billion in virtual assets from Binance to North Korea, using the operational tag TraderTraitor. An initial investigation released by Binance noted that a development operations engineer's computer may have been compromised, and the attacker subsequently gained access to service containers and submitted unauthorized withdrawal transactions; the platform stated that no evidence of wallet private key leakage had been found at that time.
The investigation is still ongoing.
From a recruiting test to the exchange's wallets, employee devices, and vendor systems, North Korea-related cyber operations have continuously infiltrated the workflows of the cryptocurrency industry.
The most familiar name to the outside world is Lazarus, the Lazarus Group. But what kind of people are behind this name, and how do they turn the assets on the screen into money that can be utilized in reality?
How Much of the North Korean Intelligence System Can Be Seen Behind Lazarus
Lazarus easily evokes the image of an independent secret team: with a fixed leader, defined members, and a little-known operations room. However, the materials we can read mostly come from sanction documents, judicial investigations, victim retrospectives, and tracking by security companies.
This name is mainly a label used for identifying network activities externally, and it may not be the official department name within North Korea.
In 2019, the U.S. Treasury Department sanctioned Lazarus, Bluenoroff, and Andariel, declaring them to be controlled by North Korea's Reconnaissance General Bureau. The Reconnaissance Bureau is an important intelligence agency in North Korea, abbreviated in English as RGB. That announcement also linked Lazarus to the 110 Research Center, which is subordinate to the third bureau of the Reconnaissance Bureau. Another sanctions announcement in 2023 continued to disclose relationships between the Technical Reconnaissance Bureau, the 110 Research Center, and Pyongyang Automation University: some institutions are responsible for cyber operations and tool development, and there are specialized schools nurturing technicians who later enter related units.
Putting these materials together reveals a supply chain of personnel with training and organizational support. As for the commonly seen online assertions like "so-and-so bureau has so many people" or "all hackers are directed by a certain department," the public evidence is far from that complete.
Rather than drawing what seems like an accurate secret organizational chart, it may be better to look down the line from those who have already surfaced.
Park Jin-hyuk is one of them.
In 2018, the U.S. Department of Justice announced criminal charges against him, stating he had worked for Chosun Expo Joint Venture. This company, which presents itself as a technology entity, was identified by U.S. authorities as a front for the North Korean government, involved in supporting malicious cyber operations. The indictment published in 2021 added two North Korean programmers, identifying all three as members of units related to the Reconnaissance Bureau.
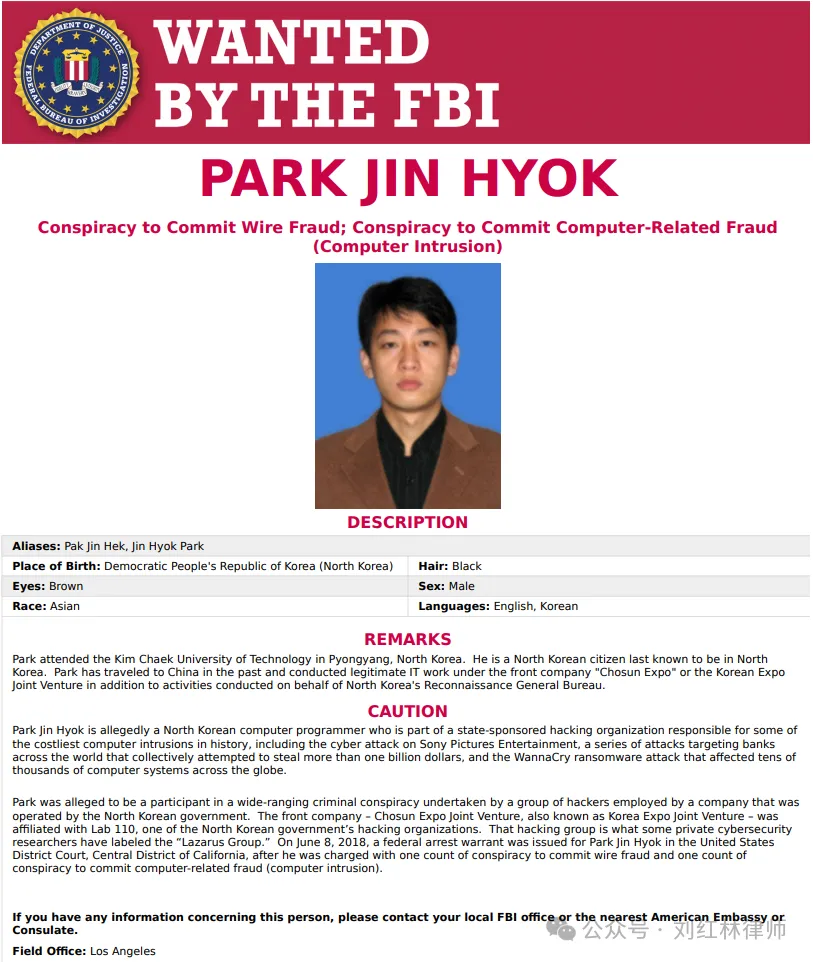
Wanted information for Park Jin-hyuk in 2018. Source: FBI/Wikimedia Commons Archive
These are accusations from the prosecution, but they provide more specific clues than just "genius hacker": a person may have a company identity, a work email, and external technical operations while being implicated in state-sponsored cyber activities.
The clients may only encounter a programmer who can take projects and write code. According to the prosecution materials, Park Jin-hyuk and his compatriots indeed did programming work for paying clients abroad; these external operations coexisted with the cyber attacks they were implicated in.
In the Park Jin-hyuk case, the U.S. referred to Lazarus as the name of the team he belonged to; in the DMM and Bybit cases, the FBI used the name TraderTraitor. Adding to this are names commonly seen in reports, such as Bluenoroff, Andariel, and APT38 (APT is short for "Advanced Persistent Threat"), making it easy for readers to think that behind each name lies a corresponding department and a fixed team.
This cyber force has never only been about stealing coins.
The destructive attack on Sony Pictures in 2014, the theft from the Central Bank of Bangladesh in 2016, and the spread of the WannaCry ransomware in 2017 later appeared in U.S. charges and attribution materials against North Korean-related individuals. Political revenge, destruction, intelligence gathering, and fundraising emerged in various cases. The cryptocurrency industry later became a significant target, precisely because it addressed the most easily monetizable need: to get money.
From Bank Transfers to Huge Assets in Cross-Chain Bridges
The Bangladesh Central Bank case has already shown the financial objectives of such actions. According to the accusations disclosed by the U.S. Department of Justice, the attackers compromised the bank's network and sent fraudulent interbank payment instructions, ultimately resulting in about $81 million being stolen.
However, the theft of traditional funds requires that after the money enters traditional banking systems, it passes through accounts, recipient institutions, and subsequent transfers before it can actually be taken.
Cryptographic assets provide a radically different possibility. If attackers gain the authority to issue valid transactions, they may transfer assets to addresses they control within a very short time. Of course, the coins still need to be exchanged for fiat currency or used to purchase supplies, which will still encounter real-world trading counterparts.
Yet, the step of "first transferring the assets away" can be carried out without relying on traditional financial institutions, which is the freedom most celebrated in the cryptocurrency world represented by Bitcoin.
North Korean-related attackers entered this market using a particularly patient approach early on: creating what seemed to be a normal cryptocurrency trading software and waiting for practitioners to install it themselves.
In 2021, the U.S. Cybersecurity and Infrastructure Security Agency, FBI, and Treasury jointly disclosed the malicious activities of AppleJeus.
AppleJeus is the name that security agencies gave to these types of software. Attackers approached targets through seemingly legitimate corporate websites and trading applications, allowing users to inadvertently bring malicious programs into their computers while searching for trading tools. For those who need to manage trading accounts, wallets, or corporate technology systems, a single software installation could bring risks from personal devices next to the company's assets.
By 2022, a larger pool of funds appeared among the targets: cross-chain bridges.
Cross-chain bridges help users transfer assets between different blockchains. Some bridges will first lock assets on one side and then provide corresponding receipts or assets on the other side. This allows users to use funds across chains, and the bridge itself gathers a large amount of assets used to support these receipts. For attackers, finding enough permission to approve disbursements presents an opportunity to access a large sum of money that many users rely on together.
In March 2022, the Ronin network serving the blockchain game Axie Infinity was hacked, resulting in losses including 173,600 ethers and 25.5 million USDC.
The most memorable aspect of this breach is that the attackers obtained signature permissions from five of the nine validators. The system originally required a certain number of validators' approvals to execute withdrawals; when attackers had enough valid signatures, the forged withdrawal request bypassed that threshold. The FBI subsequently attributed the case to Lazarus and APT38-related actors.
When people discuss blockchain security, they often first look at algorithms and contract codes. The Ronin case reminds us to also consider who keeps the signatures, where permissions are concentrated, and whether there are independent barriers between approval layers. Protocols can strictly enforce rules, but the permissions behind the rules may be taken away first.
In the same year, the Horizon cross-chain bridge of Harmony experienced a theft of about $100 million in assets. In January 2023, the FBI publicly attributed the case to the North Korean-linked Lazarus organization. Later, Atomic Wallet, Alphapo, CoinsPaid, and other wallet and payment services also appeared in the FBI's attribution announcements.
The changes in targets are significant. The attackers are no longer just chasing specific exchanges, but rather the various key entry points through which cryptocurrency assets pass: where they are stored, who approves transfers, which software is responsible for presenting transactions, and which service providers have the opportunity to touch on crucial operations. Those who stand in these roles in the work could potentially be chosen.
DMM and Bybit: First Approach Authorized Personnel
Returning to the Ginco employee mentioned at the beginning of the article, he was not an employee of DMM Bitcoin but was standing on the service chain DMM relied on for funds management. The attacker approached him under the guise of recruiting, obtaining not just an ordinary social account, but also an opportunity to further penetrate the wallet service provider.
According to the process disclosed in the joint announcement by Japan and the United States, after the interaction in March 2024, the attacker used session information to impersonate an employee after mid-May, gaining entry into Ginco's communication system. By late May, they likely manipulated the normal transaction requests of DMM employees through this access point. A few months were used to connect what appeared to be an inconsequential recruitment contact to true actions capable of transferring assets.
This is much more complex than "an employee clicked on a phishing link." The recruiter needed to make the test seem credible, and after infiltrating the device, they had to understand the work system, locate the links related to client transactions, and allow erroneous requests to pass through. An engineer's technical capability does not automatically substitute for independent verification of the recruit's identity, device isolation, and transaction requests.
On February 21, 2025, around $1.5 billion in virtual assets were stolen from Bybit, again highlighting the issue of cold wallets.
Cold wallets generally refer to arrangements that isolate the critical signing materials from everyday online environments, leading many to believe that as long as assets are placed in cold wallets, attackers will find it hard to reach them.
However, cold wallet funds will eventually need to be transferred out. At that point, the signers need to see the transaction, assess it, and then execute the signature. In Bybit's recent incident, attackers specifically targeted this handover process between personnel and the systems.
Based on Bybit's public progress report and Sygnia's technical review, the attack involved the compromise of the infrastructure related to the Safe wallet, with malicious code entering the web interface used by the signers. The signers thought they were approving a normal operation, but the transactions they signed led to changes in wallet control logic, and assets were subsequently transferred. The FBI attributed the theft to North Korea on the 26th of the month, calling the related activity TraderTraitor.
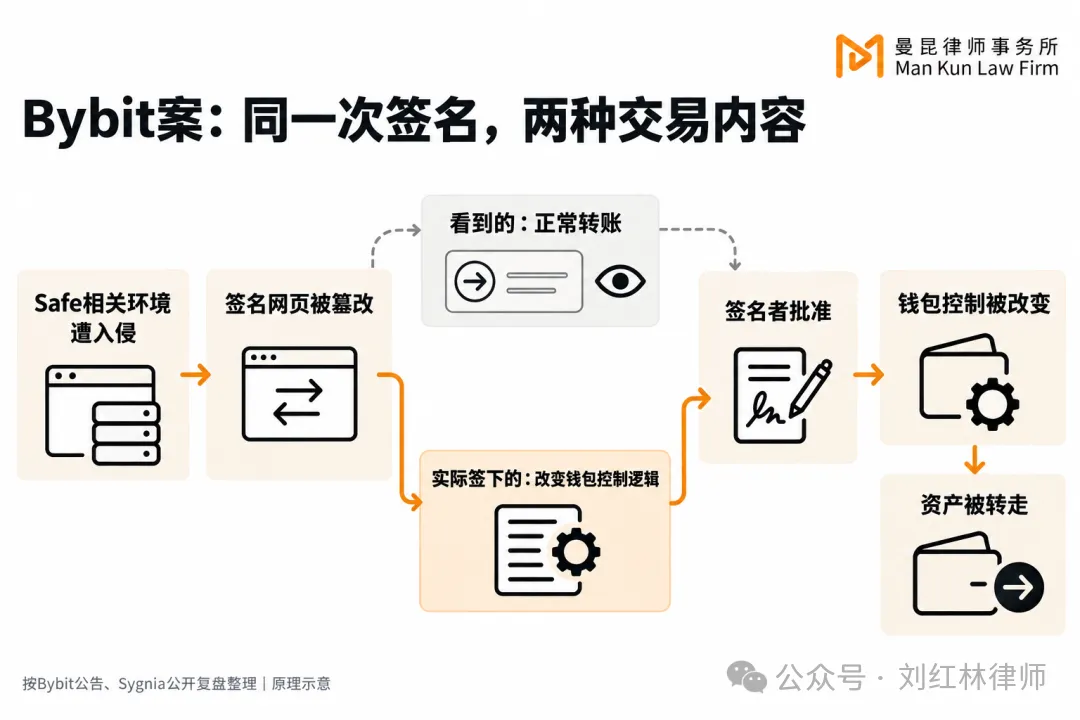
Illustration of the signature deception principle in the Bybit case
Here is a distinction that may easily be overlooked: the signature is real, but the signer's understanding of what they signed was misled. Properly secured private keys do not guarantee that every signing reflects the transaction that the custodian truly wanted to undertake. If several people rely on the same tampered display interface, multiple approvals could mistakenly repeat the same error.
In the Binance case at the end of October 2026, Binance's preliminary announcement pointed to a potential entry through the development operations engineer's computer and stated that no evidence of wallet private key leakage had been found. The FBI's announcement attributed the incident to North Korea but did not disclose the complete infiltration path.
However, drawing connections between DMM, Bybit, and this latest lead already reveals a concerning common situation: a company may focus a significant amount of energy on wallets and contracts, but attackers can enter from the employees, software pages, and operational permissions they rely on. Where the funds ultimately reside does not necessarily determine where the breach initially occurred.
More Identities of Remote Colleagues Emerge
Fake recruitment is a way to get target employees to open what attackers deliver. Another route that has been repeatedly disclosed is that attackers enter the recruitment process themselves in an effort to be hired by companies.
In June 2025, the U.S. Department of Justice announced a joint operation targeting revenue networks of remote North Korean technicians. Related cases revealed that some individuals used stolen or fabricated identities to apply for jobs, with collaborators in the U.S. receiving computers sent out by employers and allowing offshore personnel to connect remotely. The places that centralized and maintained the operation of these computers were referred to as "laptop farms."
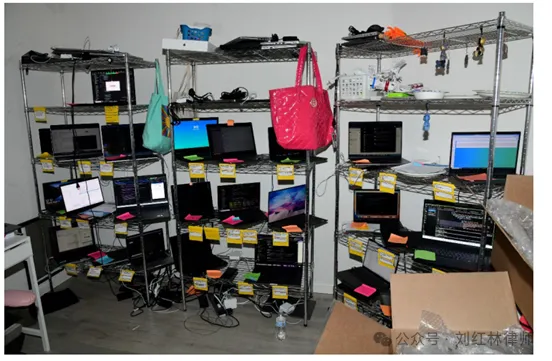
"Laptop farm" in the Chapman case: centralized storage of employer computers. Source: U.S. Department of Justice, released on July 24, 2025.
From the employer's perspective, computers shipped to local addresses and connecting via local devices make a remote colleague appear to be working normally. However, what supports this facade may be cooperation between offshore technicians, identity providers, payment arrangements, and device custodians. Impostor technicians could obtain income for North Korea-related networks by delivering work and receiving payments.
In the same round of law enforcement announcements in June 2025, one case revealed that the accused had engaged in theft after obtaining remote work for two cryptocurrency companies, using their access to assets encountered during work; one case involved modifying the source code of the employer's smart contract, resulting in a combined loss of over $900,000 for the two companies. U.S. law enforcement also warned that some impostor remote personnel would steal business data and commit extortion.
The most challenging aspect here is that companies genuinely need technical talent. Remote collaboration reduces the geographical limitations for hiring, while also making verifying identities, locations, and actual operators tougher based on a single online interview. As long as an engineer can deliver on time, the business team may gradually grant him more permissions. By the time the permissions cover code releases, production systems, or wallet operations, the gaps left by that initial identity verification will grow alongside the work.
After the Coins Are Stolen, Some People Step In
Stealing $1.5 billion in assets and acquiring $1.5 billion in freely usable cash are two different matters. Addresses may get flagged, centralized platforms may intercept deposits, and some stablecoin issuers could freeze the relevant tokens based on their permissions and rules.
So, handling funds after a coin theft is not an ancillary task, but the key to whether the entire operation can yield real benefits.
The FBI mentioned in the Bybit case announcement that attackers quickly converted part of the assets into cryptocurrencies like Bitcoin, distributing them across many addresses on multiple chains.
These actions increase the difficulty of tracing and intercepting, yet they do not make historical transactions automatically disappear. For attackers, after on-chain transfers, there's still the question: who is willing to accept these assets, give them fiat currency, or help them complete payments in real-world scenarios? At this moment, those who control exchange channels, accounts, and business contacts become important.
In 2020, the U.S. Department of Justice indicted Tian Yanyan and Li Jiadong, Chinese nationals, accusing them of laundering over $100 million in cryptocurrency assets for North Korean-related attackers. Prosecutorial materials state that the relevant funds primarily came from stolen exchanges, with the two providing paid fund transfer services through accounts and transfers. The case materials also asserted that some of the laundered funds were used to pay for the infrastructure needed for subsequent attacks against the financial sector.
This is an allegation disclosed by prosecutors, but it pushes the boundaries of the "hacker organization" further outward. Those who take the assets need to understand technology, while those who take over the assets may be more familiar with account openings, currency exchanges, and payments. A stolen coin might support the cost of the next round of operations. Solely tracking the programmers executing the breaches does not explain why this operation can continuously function.
The case of Tian Yanyan and Li Jiadong also illustrates that recovering stolen assets requires more than just tracing where the coins flowed. After money flows from the stolen exchange into exchange accounts, investigators must check who is using those accounts and the connections between the recipients and the intruders to link the theft and laundering stages. To further establish that the attack is from a North Korean-related organization, clues beyond just the funds must be connected.
In the materials released for the Park Jin-hyuk case, the U.S. listed clues including email addresses and aliases reused in different attacks, similar malicious codes, and access records of the relevant accounts. On-chain financial records also need to be cross-verified with account, device, and real-person clues to gradually trace who was operating. Looking solely at a string of wallet addresses does not reveal the operator's nationality.
These investigative materials bring some personnel and collaborative methods to the surface, but a complete internal list is still not in sight. Some attribution announcements only disclose conclusions and related addresses without revealing all the investigative basis. Understanding Lazarus has thus gradually accumulated through case after case: we can see how they approach targets and how they transfer money, but we still cannot claim that we have fully grasped the entire organization.
Conclusion
The cryptocurrency industry uses an open network to enable trading and collaboration between strangers, which we refer to as an open cooperative network. However, related North Korean operations remind us that this network is also open to organized attackers: they can seek entry points in the same job market and then make use of the funds in the same financial market. A country under financial sanctions can also leverage the efficiency of global markets to continue funding its operations.
The openness and freedom of the cryptocurrency world always come at a silent cost for someone.
免责声明:本文章仅代表作者个人观点,不代表本平台的立场和观点。本文章仅供信息分享,不构成对任何人的任何投资建议。用户与作者之间的任何争议,与本平台无关。如网页中刊载的文章或图片涉及侵权,请提供相关的权利证明和身份证明发送邮件到support@aicoin.com,本平台相关工作人员将会进行核查。


