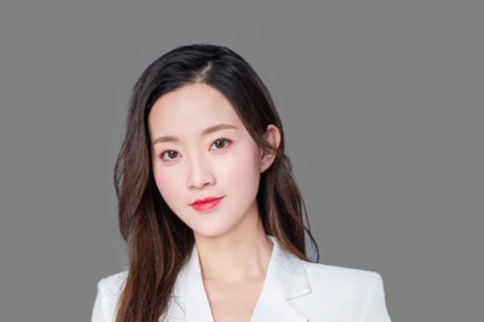
In a trust crisis triggered by a platform security incident and internal permission management issues, Binance has been thrust into the spotlight, with persistent questioning in the Chinese community about "whether funds are safe and who can access which permissions." On November 4, co-founder He Yi chose to respond comprehensively on X (formerly Twitter), making her stance clear in a lengthy post: user fund security is Binance's primary responsibility. If there is any shortfall or loss of funds, it will be wholly covered by Binance, which will not evade responsibility through bankruptcy or other legal means. This is not only a contract to users but also a positive statement to the outside world on "whether Binance will cover losses." Regarding this commitment, she admitted the company is not perfect but has been continuously evolving, openly accepting all criticism about platform security and permission management, and provided two main follow-up lines: one locks the question of "whether user funds are affected" to the answer of "fully covered by Binance," while the other announces that Binance has restructured its department access and security permission system, and will provide a report explaining "how the issues occurred," aiming to offer references for the entire industry to cope with social engineering attacks and risks related to AI permission boundaries while transparently disclosing the details of security incidents. Several Chinese media outlets, such as Odaily Planet Daily, Deep Tide TechFlow, and BlockBeats, subsequently reported on this statement, making "fully covering user losses" and "restructuring the permission system" the two core coordinates for re-evaluating Binance and He Yi after this permission storm.
Full compensation for any shortfall: Binance bets on credibility
In the midst of this trust crisis, He Yi emphasized the most critical point: user fund security is Binance's primary responsibility. Once there is a shortfall or loss of funds, it will be "fully covered by Binance" without passing the risks onto users. For traders already stirred by the security incident, this is not an abstract value proposition but a commitment to redefine the platform relationship—from "fund custodian" to "final guarantor." By clearly articulating the most extreme risk scenario, it directly counters the external fear of "will Binance deny responsibility if something goes wrong," and allows this commitment to quickly be captured by multiple Chinese crypto media outlets, becoming a highlighted phrase in their reporting.
More narratively compelling is the comparison she provides: legally, if the shortfall is significant enough, a company can completely evade responsibility through bankruptcy and other procedures, which is a viable "legal defense" seen in many traditional cases. However, she explicitly stated that Binance would not take this route but instead choose to be user-centric, binding itself more tightly with a spirit of self-restraint and contractual obligation. By stating "we could choose not to compensate" in black and white but then publicly opting for "even so, we will compensate," it sets up a flag in the competitive landscape of centralized platforms—whoever dares to write their guarantee publicly becomes more qualified to talk about trust in the next security crisis. This heavy statement also sets a higher and harder-to-retreat scrutiny standard for Binance regarding any future mistakes.
From permission imbalance to reconstruction: Major internal adjustments at Binance
If "full guarantee" represents a commitment to the result, then what truly hurts the industry in this storm is the "invisible boundary" during the process—who within Binance can access which systems, modify which data, and bypass which risk controls. The sharpest external criticisms target not a single vulnerability but the overall permission design: Are there accounts holding significant centralized power? Is there cross-departmental or cross-functional overreach space? If internal accounts are compromised by social engineering, can attackers remain hidden in permission gray areas for extended periods? These questions form the backdrop of the trust crisis.
The core corrective action He Yi threw out in her response was the announcement that Binance has restructured its access and security permission system across departments and clearly stated that "how the issues occurred" will be explained in subsequent reports. The research brief did not disclose the specific technical schemes, implementation paths, or attack vectors of this new system, but for any large platform, such restructuring often means dismantling key permissions previously concentrated in the hands of a few, layering them, and pushing sensitive operations to stricter approval chains and log audits to reduce the risks of single-point failures and “insider + external breach” combinations. He Yi also emphasized that the details of this security incident will be made public, aimed at providing references for the entire industry in dealing with social engineering attacks and permission boundary risks related to AI. For Binance, this is not only a remedial topic but also a public examination question—whether this permission reconstruction can meet expectations will become a crucial benchmark for the external assessment of whether Binance has truly stepped out of the shadow of "permission imbalance."
Exposing wounds: turning security incidents into public goods for the industry
In this sudden trust crisis, the instinctive reaction of most platforms is often to “suppress the matter” to avoid amplifying panic. In her response on November 4, He Yi chose the opposite path—she publicly acknowledged that Binance experienced a security incident and stated clearly that Binance would choose to disclose the specific details of this event, hoping to transform the "incident report" that originally circulated only internally into a visible explanation for users through transparency. She directly linked this choice to trust: not relying on a simple statement of "fund security" to make the dispute fade away, but using verifiable and question-worthy disclosures to rebuild users' and the industry's judgment basis about Binance. For a platform that has just experienced a permission dispute, shifting from "concealing risk impressions" to "publicly showing its own vulnerabilities" is in itself a narrative turn.
However, in He Yi's narrative, this disclosure carries a goal beyond mere self-exoneration. On one hand, she emphasizes that reports will explain "how the issues occurred," while on the other hand, she deliberately elevates this public disclosure to a kind of "public good for the industry": what Binance has faced is not only technological vulnerabilities but also the process of how social engineering attacks infiltrate organizations and break through permission boundaries, as well as how risks related to AI permissions are triggered and misused. She hopes to present these paths and costs to provide reusable lessons for other institutions when designing permission systems and introducing AI tools. It is noteworthy that as of the time of publication, the specific nature and technical details of these security incidents have not truly been unveiled to the public; "exposing wounds" remains more of a declaration than an accomplished fact. Whether this choice will ultimately be remembered as building public goods during a crisis or as a cautious public relations attempt will depend on the depth and honesty of Binance's future disclosures.
Who is watching Binance: users, media, and the industry's response
As information has not yet fully unfolded, different groups focus on different aspects. Ordinary users primarily care about "Is my money still there?" He Yi emphasizes that user fund security is the primary responsibility and commits that if there is any shortfall or loss, it will be fully covered by Binance, without evading responsibility through bankruptcy or other means. In the context of damaged trust, this statement is seen by many as the last line of defense. For them, the complex permission system and internal processes remain quite abstract; what they can understand and what gets first relayed is the straightforward promise of "we'll cover the losses."
Media and industry observers have a slightly longer response arc. Several Chinese crypto media outlets, such as Odaily Planet Daily, Deep Tide TechFlow, and BlockBeats, almost simultaneously captured two main axes from He Yi's statement: one is that Binance will fully cover user losses, and the other is that the access and security permission system has been restructured. This high degree of consistent reporting angle quickly amplifies this response in the Chinese crypto space into a model case of "security and permission": on one side is a clear compensation commitment, and on the other is a reform blueprint with details still not fully disclosed. In the gap before the specific technical report is released, the market can only gauge Binance's sincerity through these two points—greater commitments lead to more room for questioning; the vaguer the permission restructuring is articulated, the more likely industry will treat it as a benchmark for future evaluation. Thus, a yet-to-be-unveiled security incident is frozen into a debate about "to what extent can promises be fulfilled" and "whether evolution is genuinely occurring."
After the storm: How much trust can be regained through responsibility commitments
From the trust crisis triggered by security and permission management to He Yi stepping out to acknowledge issues on November 4, emphasizing that user fund security is the primary responsibility, and publicly stating that any shortfall will be fully covered by Binance without evading through bankruptcy, the narrative focus has shifted from "Did something happen?" to "If something happens, who is responsible?" On the same timeline, Binance announced the restructuring of the access and security permission system, extending responsibility commitments to governance structure levels, hoping that permission reconstruction and future report disclosures will mitigate current trust depreciation. In the short term, this stance of "fund coverage + accepting all criticism" indeed sets a lower limit for panic emotions, but its support for long-term trust depends on two unresolved blanks: the research brief clearly points out that the specific nature of the current security incident, occurrence time (apart from the response date of November 4), involved amounts, and the affected range have not been publicly disclosed, while the so-called permission restructuring remains only at a principled explanation level. Up to now, Binance's core actions are locked in the four points of "open acknowledgment of issues, commitment to fund responsibility, restructuring permission systems, and planning for detailed report release." What the market will look for next is whether the report truly answers "Are user funds affected?" and "How did the issues occur?" as well as whether the new permission structure is practically embodied as verifiable constraints and not merely a story existing in announcements.
Join our community to discuss and grow stronger together!
AiCoin exclusive Hyperliquid benefits: https://app.hyperliquid.xyz/join/AICOIN88
AiCoin exclusive Aster benefits: https://www.asterdex.com/zh-CN/referral/9C50e2
On-chain Telegram community: https://t.me/AiCoinWhaleData
On-chain community: https://www.aicoin.com/link/chat?cid=N6OVMor5g
AiCoin on-chain Twitter: https://x.com/aicoinwhaledata
免责声明:本文章仅代表作者个人观点,不代表本平台的立场和观点。本文章仅供信息分享,不构成对任何人的任何投资建议。用户与作者之间的任何争议,与本平台无关。如网页中刊载的文章或图片涉及侵权,请提供相关的权利证明和身份证明发送邮件到support@aicoin.com,本平台相关工作人员将会进行核查。